

Set Up SAML SSO for Okta
Who can use this feature
Anyone with these permissions: Manage SAML group access
This article explains how to set up Eon’s Okta integration from the Okta catalog. After completing this process, users who are members of the groups you’ve mapped can log in to Eon using SAML SSO.
If you’ve already configured SAML and want to adjust groups, skip to Map SAML groups in Eon.
Configure Okta SAML SSO
You’ll find the SAML SSO page under Access management in your global management console in Eon. Identity providers and their group mappings are both on this page.
Supported Okta features
The integration uses Okta’s SP-initiated SSO feature, which means your users sign in to Eon from Eon’s login page rather than from the Eon tile in Okta. Clicking the tile in Okta brings users to their Eon login page.
Before you start
Before you start, make sure:
-
You’re an Okta administrator.
-
You have the permissions in Eon mentioned at the top of this article.
-
There’s a role that has the exact permissions you want to grant to the group. If there isn’t one, you can create a custom role.
Copy Eon's service provider details
In Eon, go to the SAML SSO global management page. Click Add Identity Provider. Once you have at least one identity provider, this button is a icon in the header of the Identity providers panel.
The Add identity provider dialog lists Eon’s service provider details, which you’ll paste into Okta, each with a copy button. Keep the dialog open because you’ll need these values in the next step.
Configure the SAML integration in Okta
-
Click Add Integration. Okta’s account selection page is opened.
-
Choose your Okta organization and log in.
-
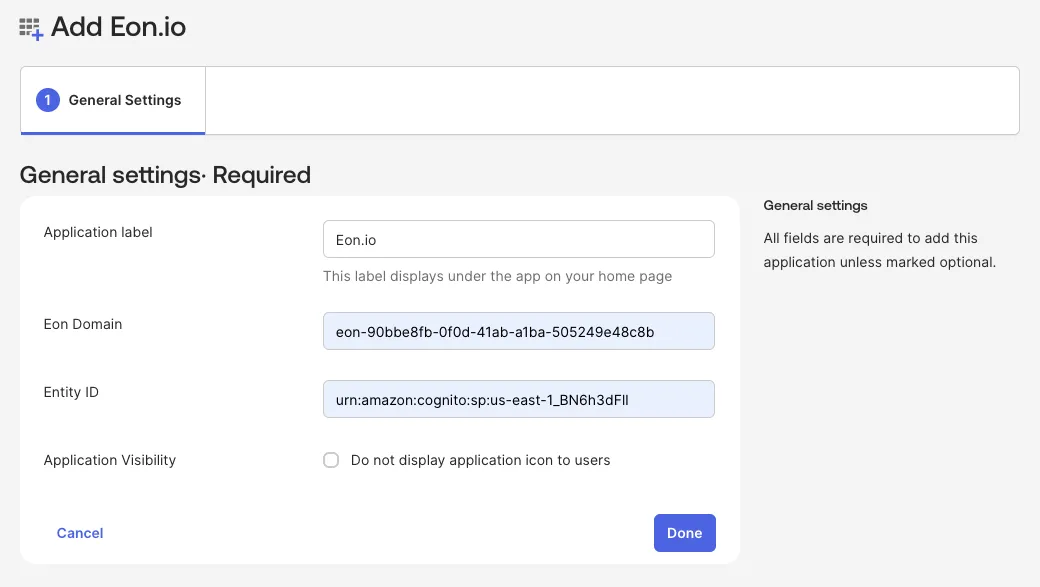
In the app’s General settings page, fill in the form:
-
In Application label, give a meaningful name, such as
Eon.io. -
Copy Eon’s service provider details from the Add identity provider dialog you left open in Eon:
-
In Application Visibility, leave Do not display application icon to users unselected.
-
-
Click Done.
The app is created and you’re redirected to Okta’s app information page.
Add user groups to the claim
Configure the app to send user group membership with the SAML assertion so Eon can map users to the correct roles.
-
In the Sign On tab, in the Settings section, click Edit.
-
In the Configured SAML Attributes section, set groups to Matches regex and type
.*in the text box.If too many groups are sent with the SAML assertion, the request can become malformed and cause login failures. As a best practice, filter the groups sent to only those relevant to the Eon app. For example, use a regex pattern like
^EON_.*to send only groups that start withEON_. -
Click Save.
Assign the Okta app to user groups
Assign the Eon app to user groups to control which users can access Eon through SAML SSO.
In the Assignments tab, click Assign > Assign to Groups. Choose the groups you want to be able to access Eon.
Copy the SAML settings to Eon
Return to the Add identity provider dialog in Eon.
-
Give a meaningful Display name, such as
Okta. You can’t change it later, so pick a name you’ll recognize. -
Provide the corresponding SAML details from Okta. You can find these settings in the Sign On tab by expanding More details:
ImportantEon requires the entire contents of the certificate, including the
BEGIN CERTIFICATEandEND CERTIFICATElines. Copying the signing certificate directly from Okta omits these lines, so you’ll need to download the certificate and copy its contents from the.certfile. -
Click Add Identity Provider.
Map SAML groups in Eon
Although SAML SSO is now enabled on your Eon account, SAML users can’t log in yet because they have no Eon access by default. To grant access, you need to map your SAML groups in Eon.
Click Add Group Mapping. The New group mapping dialog opens.
Set these options:
-
SAML identity provider: Choose the Okta identity provider you just added.
-
Group ID: Enter the group’s ID your identity provider passes in the SAML assertion. This must be an exact match with the assertion. This is case-sensitive, so
eon viewersandEon viewersare different groups.Okta uses the group’s name as the group ID.
-
Label: Optionally, give the group a display name so it’s more recognizable in Eon.
Then choose the roles you want to assign to the group. You can assign multiple roles.
Click Create.
SAML configuration changes can take up to 15 minutes to take effect.
Eon-initiated login
After setup and group mapping, your users can log in to Eon using their Okta credentials. Let them know and share these directions with them:
-
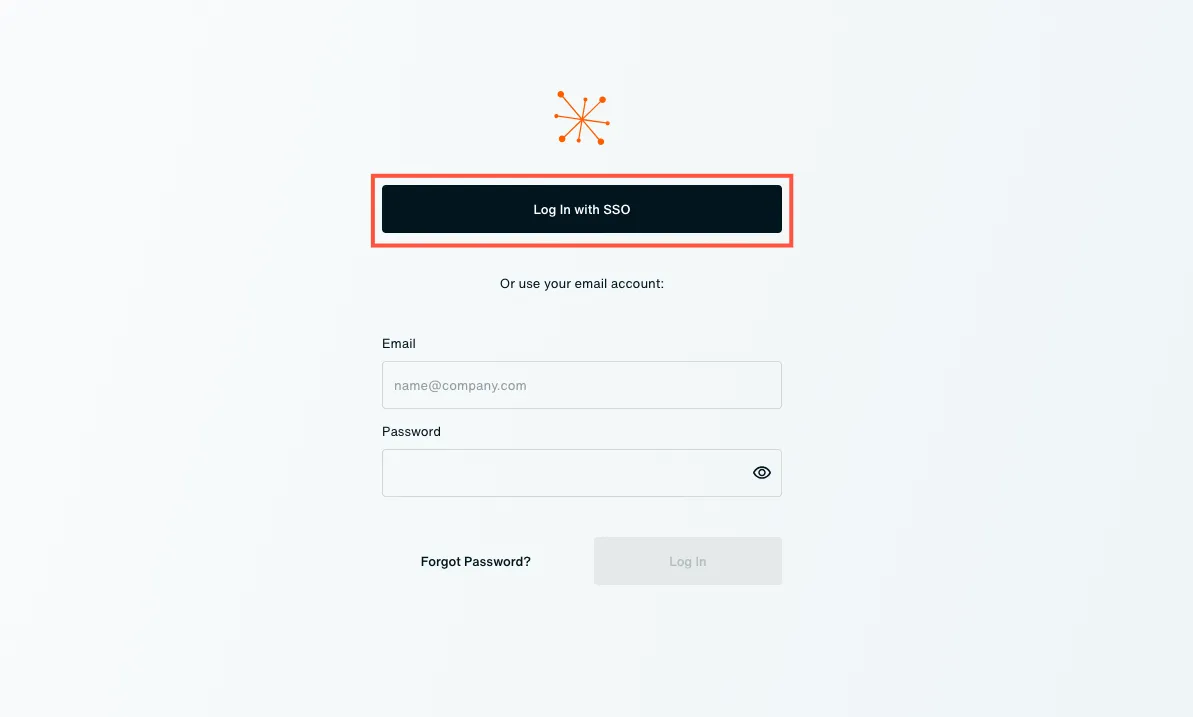
Go to your Eon domain’s login page (for example,
https://your-company.console.eon.io/login). -
Click Log In with SSO. Enter your Okta credentials and sign in.
On successful login, you’re redirected to the Eon console.